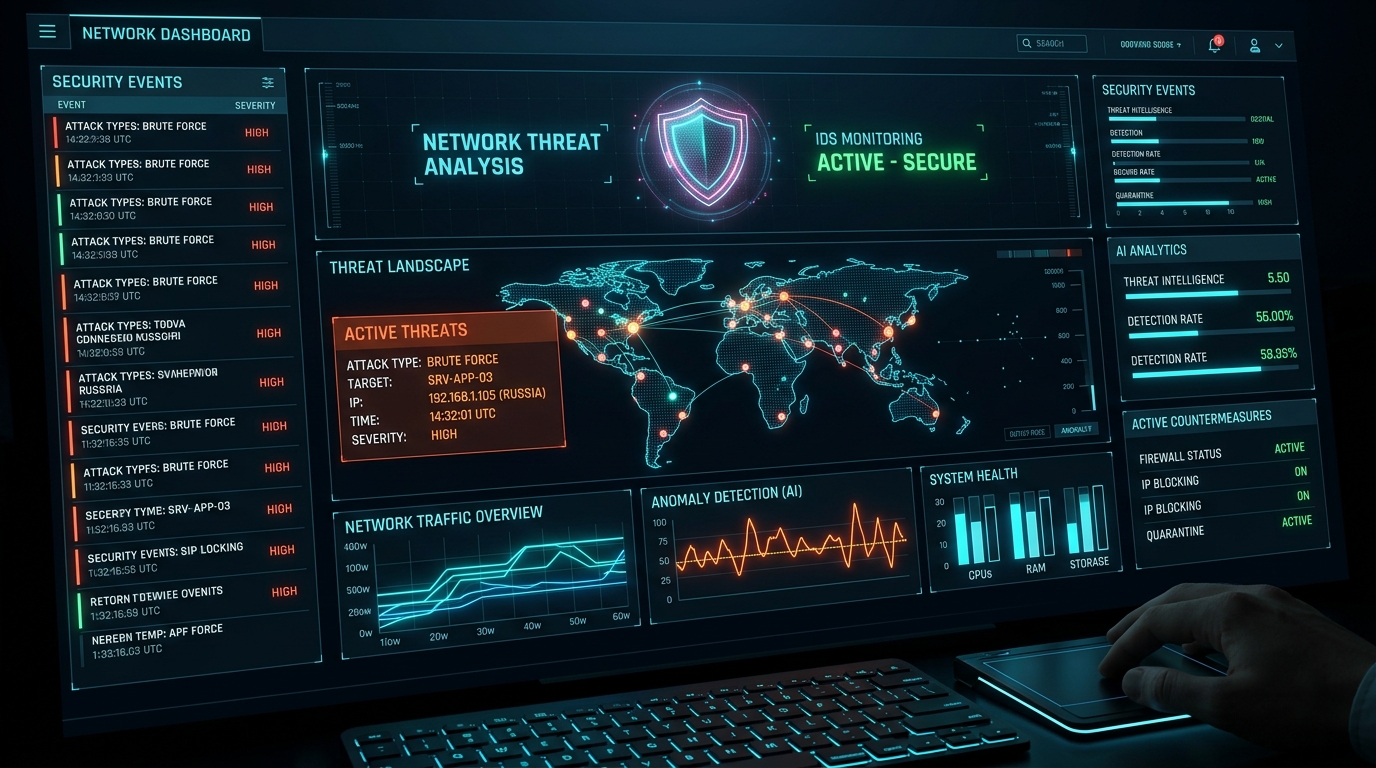
Zyris IDS System
Problem: Modern organizations face an increasing number of sophisticated cyberattacks, making it difficult to detect malicious network activities in real time. Traditional intrusion detection systems often suffer from high false positives, limited visualization capabilities, and a lack of explainable threat insights, delaying effective incident response.
Approach: Developed Zyris, an AI-powered Intrusion Detection System (IDS) that combines machine learning with an interactive Security Operations Center (SOC) dashboard. The platform performs real-time network traffic analysis, attack classification, anomaly detection, and threat visualization while presenting actionable security insights through an intuitive, production-ready web interface.
Outcome: Successfully deployed a scalable IDS dashboard that provides real-time threat monitoring, AI-driven anomaly detection, interactive attack analytics, and system health visualization. The application delivers a responsive user experience with fast performance, enabling security teams to monitor, analyze, and respond to cyber threats efficiently.